A Cloud Engineer resume should name the provider, infrastructure and operating responsibilities you actually held. Show how you changed and supported environments with application, security and networking colleagues. A list of every cloud service cannot establish production experience or prove availability.
These previews use the same layouts as the builder, with identical example content. Open a full preview to inspect the text and spacing.
Fictional candidate, employers, education and results. The optional portrait is AI-generated. Use your own evidence and photo; the example is not inserted into your resume.
Harbor
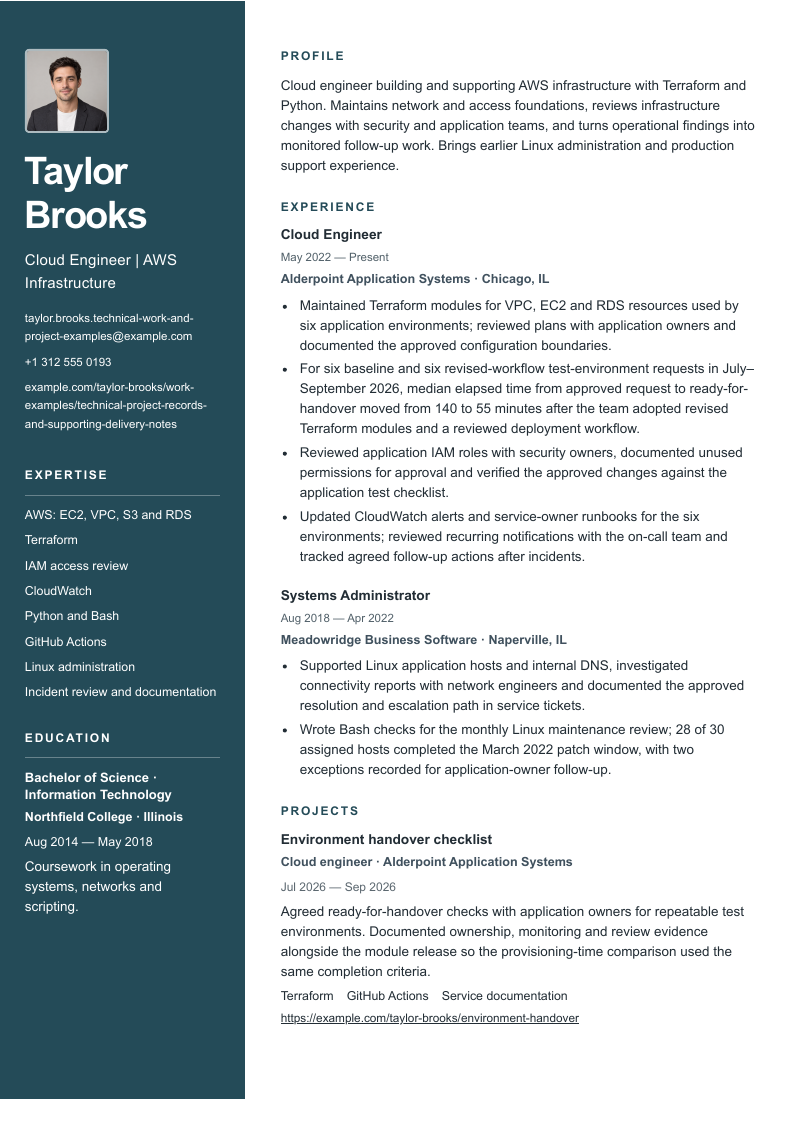
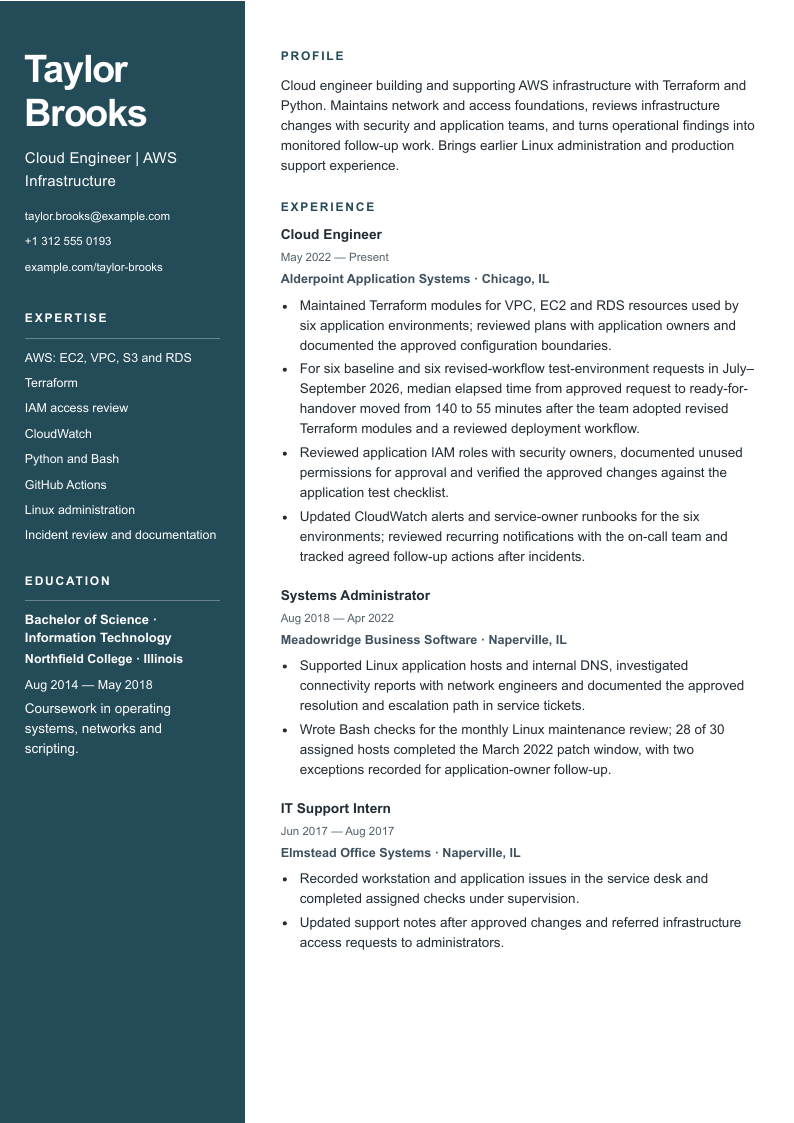
A dark left identity rail carries contact details, skills and education beside a white profile, experience and project column.
Before sending: The rail is narrow; check long contacts, skills and education with both photo settings and read copied text order.
“Use” opens signup with that design and photo preference selected for the builder. A free account is required. Free-plan PDF downloads include a watermark; see current plans for paid options. Photo conventions vary; follow the employer’s instructions and local expectations.
A dark left identity rail carries contact details, skills and education beside a white profile, experience and project column. A white centered header places an optional circular portrait above the identity and a restrained single-column record. Small square section markers and colored headings organize a single-column record with a date gutter.
Each design shows the same fictional career. The default has no photo; the optional portrait is AI-generated. The buttons retain the exact selected design, photo preference and Cloud Engineer role through signup. They do not put the example career or portrait into your account. A free account is required; free-plan PDF downloads include a watermark. These images show paid-plan output.
Taylor Brooks, the employers, college, career, dates and results are original fiction. All example.com links are placeholders and the 555 phone number is fictional. Use the structure with your own supported facts.
Cloud engineer building and supporting AWS infrastructure with Terraform and Python. Maintains network and access foundations, reviews infrastructure changes with security and application teams, and turns operational findings into monitored follow-up work. Brings earlier Linux administration and production support experience.
Skills
AWS: EC2, VPC, S3 and RDS · Terraform · IAM access review · CloudWatch · Python and Bash · GitHub Actions · Linux administration · Incident review and documentation
Experience
Cloud Engineer
Alderpoint Application Systems · Chicago, IL
May 2022–Present
Maintained Terraform modules for VPC, EC2 and RDS resources used by six application environments; reviewed plans with application owners and documented the approved configuration boundaries.
For six baseline and six revised-workflow test-environment requests in July–September 2026, median elapsed time from approved request to ready-for-handover moved from 140 to 55 minutes after the team adopted revised Terraform modules and a reviewed deployment workflow.
Reviewed application IAM roles with security owners, documented unused permissions for approval and verified the approved changes against the application test checklist.
Updated CloudWatch alerts and service-owner runbooks for the six environments; reviewed recurring notifications with the on-call team and tracked agreed follow-up actions after incidents.
Systems Administrator
Meadowridge Business Software · Naperville, IL
August 2018–April 2022
Supported Linux application hosts and internal DNS, investigated connectivity reports with network engineers and documented the approved resolution and escalation path in service tickets.
Wrote Bash checks for the monthly Linux maintenance review; 28 of 30 assigned hosts completed the March 2022 patch window, with two exceptions recorded for application-owner follow-up.
Education
Bachelor of Science in Information Technology · Northfield College · Illinois
August 2014–May 2018
Coursework in operating systems, networks and scripting.
Projects
Environment handover checklist
Cloud engineer · Alderpoint Application Systems
July 2026–September 2026
Terraform · GitHub Actions · Service documentation
Agreed ready-for-handover checks with application owners for repeatable test environments. Documented ownership, monitoring and review evidence alongside the module release so the provisioning-time comparison used the same completion criteria.
Taylor’s record is AWS infrastructure with Terraform, IAM review, network collaboration, monitoring and earlier Linux operations. It does not imply equivalent experience in Azure and Google Cloud, or ownership of every SRE responsibility. Name providers and services you have used, then show the infrastructure change or operating decision behind them.
The primary employer examples have different boundaries. DRW’s Chicago role covers hybrid and multicloud foundations with AWS depth and five-plus years of relevant experience. The Quality Group’s AWS role is mid–senior and remote within Germany, with current primary residence required. Momentum’s Hyderabad remote role asks for substantial AWS, Terraform and production-code experience. None establishes that every cloud role requires the same provider mix, location or certification.
Infrastructure bullets should show resources, environment scope, change review and consumers. Network design, IAM policy approval, incident command and spending commitments are distinct authorities. Describe the part entrusted to you and who reviewed the work. A support role can demonstrate strong judgment without being recast as enterprise cloud architecture.
Six annotated Cloud Engineer bullet rewrites
These examples show how to make scope and evidence assessable. The after statements are exactly the six work-history bullets in the base resume. Replace every invented fact; do not borrow a metric you cannot support.
1. Define the infrastructure delivered
Before: Built the entire cloud from scratch.
After: Maintained Terraform modules for VPC, EC2 and RDS resources used by six application environments; reviewed plans with application owners and documented the approved configuration boundaries.
Why it works: The resources, consumers and review authority establish scope without implying ownership of every cloud service.
Evidence to check: Module inventory, environment count, reviews and configuration responsibility.
2. Give provisioning time a fair comparison
Before: Provisioned everything instantly.
After: For six baseline and six revised-workflow test-environment requests in July–September 2026, median elapsed time from approved request to ready-for-handover moved from 140 to 55 minutes after the team adopted revised Terraform modules and a reviewed deployment workflow.
Why it works: Defines 12 requests, period and measurement endpoints; the team workflow shares credit and the result is not a production guarantee.
Evidence to check: Request timestamps, readiness criteria, comparable resource scope, baseline sample and team contributions.
3. Show access work without exposing it
Before: Made AWS completely secure.
After: Reviewed application IAM roles with security owners, documented unused permissions for approval and verified the approved changes against the application test checklist.
Why it works: Shows access review and controlled validation without claiming universal security or publishing sensitive policies.
Evidence to check: Sanitized review scope, approval responsibility and test outcome; exclude identifiers and policy contents.
4. Connect monitoring to operational decisions
Before: Guaranteed 99.99% uptime.
After: Updated CloudWatch alerts and service-owner runbooks for the six environments; reviewed recurring notifications with the on-call team and tracked agreed follow-up actions after incidents.
Why it works: Monitoring, ownership and follow-up are observable responsibilities. They do not prove an availability percentage.
Evidence to check: Alert ownership, review period, permitted incident themes and action records.
5. Make networking scope concrete
Before: Expert in every cloud network.
After: Supported Linux application hosts and internal DNS, investigated connectivity reports with network engineers and documented the approved resolution and escalation path in service tickets.
Why it works: The earlier role supports infrastructure progression while preserving network-team authority.
Evidence to check: Actual systems supported, ticket responsibilities and cross-team decisions.
6. Separate maintenance completion from resilience
Before: Automated away all outages.
After: Wrote Bash checks for the monthly Linux maintenance review; 28 of 30 assigned hosts completed the March 2022 patch window, with two exceptions recorded for application-owner follow-up.
Why it works: Names the month, host population and exceptions. Patch completion does not establish that a service cannot fail.
Evidence to check: Assigned host list, patch-window records, exception approvals and your scripting contribution.
Measure a defined infrastructure event
Taylor’s summary names AWS, Terraform, access and network foundations, reviewed changes and operational follow-up. A new applicant can lead with a labeled lab and systems background. A mid-career engineer can describe environment ownership and change practices. A senior applicant should name genuine architecture boundaries, multi-team decisions or mentoring without claiming all cloud transformation work.
The provisioning comparison has six baseline and six revised-workflow requests in one quarter. Its clock starts at approval and ends at ready-for-handover, using comparable test-environment scope. Revised modules and the team deployment workflow share credit. This is different from execution time alone, and it does not promise the same result for a production migration or a more complex request.
Cost optimization, availability and recovery results need their own evidence. For spend, compare actual periods and workload, distinguish estimates from bills and explain other contributors. For uptime or MTTR, define the service, incident population and observation window. A monitoring installation or a successful patch window cannot establish a guaranteed availability percentage.
AWS’s official IAM guidance includes least privilege and review of unused access. On the resume, Taylor describes an approved review and validation role. Keep public summaries at that level: no account identifiers, credentials, private policies, network topology or customer incident details. An access review is not evidence of full compliance certification.
Connect Cloud Engineer skills to evidence
Choose a short, relevant list from work you can explain. Use the vacancy’s wording when accurate, then support it with decisions and outcomes in the history. A keyword list cannot establish competence or guarantee screening success.
Cloud Engineer skills and supporting evidence
Skill
Evidence to gather
Fictional example
AWS infrastructure
Resources, environments and actual ownership.
VPC, EC2 and RDS modules for six environments.
Infrastructure as code
Reviewed changes and consumers.
Terraform plans reviewed with application owners.
IAM
Review scope, approvals and validation.
Unused permissions referred to security owners.
Networking
Systems and collaboration boundary.
Linux connectivity and internal DNS support.
Automation
Workflow and measurement endpoints.
Approved request through ready-for-handover.
Operations
Alerts, owners and action tracking.
CloudWatch alerts and service-owner runbooks.
List education and credentials with their real status
Taylor lists an information technology degree with operating systems, networks and scripting coursework. Use actual education and keep projects distinct from employment. Relevant systems administration experience can help explain a move into cloud engineering, but should retain its original job title and operating scope.
The fictional resume contains no certification. Momentum lists AWS and/or Azure certification for its opening; do not imply that Taylor meets that requirement. If you hold a relevant credential, check the current issuer title and record its issue date, expiry or active status accurately. A planned exam is not an earned credential, and a course completion record is not equivalent to a professional certification.
Use a labeled lab without inventing production scale
An early-career lab can show a small environment, reviewed infrastructure changes, basic monitoring and a clear handover. Use synthetic data and label the environment as practice. Explain decisions and checks in plain language; a public resume does not need credentials, live account identifiers or operational access details.
If you are moving from support or systems administration, show relevant Linux, DNS, scripting, maintenance and escalation work under the title you held. The expanded example retains an older IT support internship and adds resource-ownership and maintenance-handover projects. None turns prior workstation support into ownership of production AWS architecture.
Check a long email and portfolio URL
The long-contact Harbor export has the photo on and changes only the resume email and portfolio URL. Taylor’s user identity, phone, jobs, education and project remain identical. Check the last characters in the narrow identity rail and confirm the full link remains usable.
Cloud engineer building and supporting AWS infrastructure with Terraform and Python. Maintains network and access foundations, reviews infrastructure changes with security and application teams, and turns operational findings into monitored follow-up work. Brings earlier Linux administration and production support experience.
Skills
AWS: EC2, VPC, S3 and RDS · Terraform · IAM access review · CloudWatch · Python and Bash · GitHub Actions · Linux administration · Incident review and documentation
Experience
Cloud Engineer
Alderpoint Application Systems · Chicago, IL
May 2022–Present
Maintained Terraform modules for VPC, EC2 and RDS resources used by six application environments; reviewed plans with application owners and documented the approved configuration boundaries.
For six baseline and six revised-workflow test-environment requests in July–September 2026, median elapsed time from approved request to ready-for-handover moved from 140 to 55 minutes after the team adopted revised Terraform modules and a reviewed deployment workflow.
Reviewed application IAM roles with security owners, documented unused permissions for approval and verified the approved changes against the application test checklist.
Updated CloudWatch alerts and service-owner runbooks for the six environments; reviewed recurring notifications with the on-call team and tracked agreed follow-up actions after incidents.
Systems Administrator
Meadowridge Business Software · Naperville, IL
August 2018–April 2022
Supported Linux application hosts and internal DNS, investigated connectivity reports with network engineers and documented the approved resolution and escalation path in service tickets.
Wrote Bash checks for the monthly Linux maintenance review; 28 of 30 assigned hosts completed the March 2022 patch window, with two exceptions recorded for application-owner follow-up.
Education
Bachelor of Science in Information Technology · Northfield College · Illinois
August 2014–May 2018
Coursework in operating systems, networks and scripting.
Projects
Environment handover checklist
Cloud engineer · Alderpoint Application Systems
July 2026–September 2026
Terraform · GitHub Actions · Service documentation
Agreed ready-for-handover checks with application owners for repeatable test environments. Documented ownership, monitoring and review evidence alongside the module release so the provisioning-time comparison used the same completion criteria.
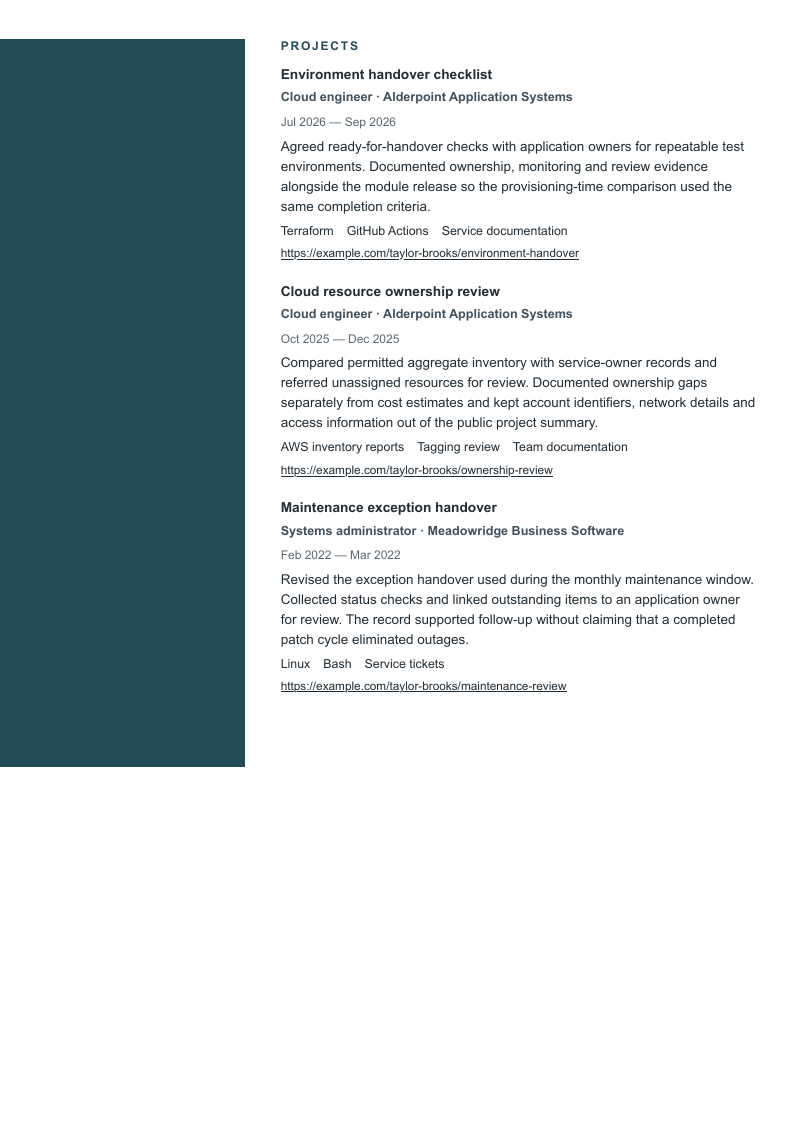
The expanded Harbor export has the photo off. It adds an IT support internship, a resource-ownership review and a maintenance exception handover, preserving every base field. Read the rail and main column through every page, especially the last project sentence and the request-to-handover qualifier.
Cloud engineer building and supporting AWS infrastructure with Terraform and Python. Maintains network and access foundations, reviews infrastructure changes with security and application teams, and turns operational findings into monitored follow-up work. Brings earlier Linux administration and production support experience.
Skills
AWS: EC2, VPC, S3 and RDS · Terraform · IAM access review · CloudWatch · Python and Bash · GitHub Actions · Linux administration · Incident review and documentation
Experience
Cloud Engineer
Alderpoint Application Systems · Chicago, IL
May 2022–Present
Maintained Terraform modules for VPC, EC2 and RDS resources used by six application environments; reviewed plans with application owners and documented the approved configuration boundaries.
For six baseline and six revised-workflow test-environment requests in July–September 2026, median elapsed time from approved request to ready-for-handover moved from 140 to 55 minutes after the team adopted revised Terraform modules and a reviewed deployment workflow.
Reviewed application IAM roles with security owners, documented unused permissions for approval and verified the approved changes against the application test checklist.
Updated CloudWatch alerts and service-owner runbooks for the six environments; reviewed recurring notifications with the on-call team and tracked agreed follow-up actions after incidents.
Systems Administrator
Meadowridge Business Software · Naperville, IL
August 2018–April 2022
Supported Linux application hosts and internal DNS, investigated connectivity reports with network engineers and documented the approved resolution and escalation path in service tickets.
Wrote Bash checks for the monthly Linux maintenance review; 28 of 30 assigned hosts completed the March 2022 patch window, with two exceptions recorded for application-owner follow-up.
IT Support Intern
Elmstead Office Systems · Naperville, IL
June 2017–August 2017
Recorded workstation and application issues in the service desk and completed assigned checks under supervision.
Updated support notes after approved changes and referred infrastructure access requests to administrators.
Education
Bachelor of Science in Information Technology · Northfield College · Illinois
August 2014–May 2018
Coursework in operating systems, networks and scripting.
Projects
Environment handover checklist
Cloud engineer · Alderpoint Application Systems
July 2026–September 2026
Terraform · GitHub Actions · Service documentation
Agreed ready-for-handover checks with application owners for repeatable test environments. Documented ownership, monitoring and review evidence alongside the module release so the provisioning-time comparison used the same completion criteria.
AWS inventory reports · Tagging review · Team documentation
Compared permitted aggregate inventory with service-owner records and referred unassigned resources for review. Documented ownership gaps separately from cost estimates and kept account identifiers, network details and access information out of the public project summary.
Systems administrator · Meadowridge Business Software
February 2022–March 2022
Linux · Bash · Service tickets
Revised the exception handover used during the monthly maintenance window. Collected status checks and linked outstanding items to an application owner for review. The record supported follow-up without claiming that a completed patch cycle eliminated outages.
Condense repeated duties before removing the definition behind a result. Use another page when relevant evidence needs it. Check for isolated headings, detached dates and qualifiers separated from metrics; page count alone cannot establish readability.
Inspect the download before applying
Keep six baseline and six revised requests with the provisioning comparison and retain team contribution.
Confirm that IAM review, monitoring and patch completion are not written as security, compliance or uptime guarantees.
Inspect the dark rail, every date and complete project ending with the chosen photo setting.
Copy text from the PDF and inspect application fields when available; follow the employer’s requested file type.
A free account is required for the builder. Free-plan PDF downloads include a watermark; the previews show paid-plan output. Template buttons retain the exact design, photo preference and Cloud Engineer role. Add your own career details and photo after signup.
The resume analyzer gives advisory feedback. For drafting help, use the bullet point generator and check every suggestion against your facts. No design guarantees parsing, interviews or a hiring outcome.
Questions, answered
What skills should a Cloud Engineer include?
Select the provider, IaC, networking, access, scripting, monitoring and operations skills you can demonstrate. AWS, Azure, GCP, Kubernetes and Docker are not interchangeable; include each only with real experience relevant to the opening.
How do I write a Cloud Engineer summary?
State the provider or infrastructure specialty, your operating scope and two or three supported strengths. Keep lab, support, production engineering and enterprise architecture experience distinct.
What are the key responsibilities of a Cloud Engineer?
Depending on the team, they include infrastructure changes, IaC, networking, identity, deployment automation, monitoring, incident follow-up and cost review. Migration, SRE, compliance and multicloud ownership require their own evidence.
What ATS keywords should a Cloud Engineer use?
Use accurate terms from the vacancy in supported context, such as AWS, Terraform, IAM, VPC, Linux, Python or CloudWatch. Add Kubernetes, Azure or GCP only if relevant to your work. Keywords and templates cannot guarantee an interview.
What makes a Cloud Engineer resume stand out?
Clear provider depth, reviewed change responsibility and defined operating measures make the work assessable. Explain measurement boundaries and collaboration instead of claiming universal uptime or savings.
How long should this resume be?
Use the space needed for relevant, readable evidence. A short early-career record may fit one page; a fuller record can need two. Check every exported page rather than shrinking the type to meet an arbitrary limit.
What happens when I choose a design?
Signup retains the exact design, photo preference and role. A free account is required. Free-plan PDF downloads include a watermark; these examples show paid-plan output. The fictional career and AI portrait are not inserted into your account.
Prepared by Resumize with AI-assisted research and drafting for English-language applications. Three primary employer descriptions were directly retrieved with full responsibilities and Apply forms on October 28, 2026: DRW in Chicago, The Quality Group’s Germany-based AWS role and Momentum’s Hyderabad remote role. These examples vary in seniority, location and provider scope. Official AWS IAM guidance supports access-review terminology. This is not a representative survey, a certification requirement for all employers or a claim that the fictional applicant qualifies for every opening. No application was submitted, private account or customer data used, or hiring outcome tested.
Read October 28, 2026. Chicago; five-plus years in production cloud and hybrid environments. AWS depth plus other-cloud exposure, networking, IAM, automation and operations. Broader multicloud scope than the fictional AWS record. Full description and Apply/application form directly retrieved with HTTP 200; no posting date displayed.
Read October 28, 2026. Mid–senior, remote within Germany with current primary residence required. AWS, Terraform, self-service, CI/CD, IAM and observability; remote does not mean worldwide. Full description and Apply/application form directly retrieved with HTTP 200; no posting date displayed.
Read October 28, 2026. Hyderabad remote; five-plus years in relevant technology work and three-plus years in several AWS/Terraform areas. Lists certifications as a vacancy requirement; this sample has no credential claim. Full description and Apply/application form directly retrieved with HTTP 200; no posting date displayed.
Read October 28, 2026. Official AWS guidance covers least privilege and review of unused access. Used for scope and terminology; the guide does not publish operational access instructions.