Harbor
A calm header and clear section hierarchy give a technical career a structured presentation.
Before sending: Read long architecture descriptions and the full contact line at normal size.
Preventive controls and exceptions · US resume context
A Security Engineer resume should connect control definitions, approved changes and remaining exceptions to your actual remit. Name evidence and system owners. Keep a configuration-check result distinct from breach prevention or complete risk reduction.
By Resumize · · AI-assisted research and drafting
Three designs · one example
These previews use the same layouts as the builder, with identical example content. Open a full preview to inspect the text and spacing.
Fictional candidate, employers, education and results. The optional portrait is AI-generated. Use your own evidence and photo; the example is not inserted into your resume.
A calm header and clear section hierarchy give a technical career a structured presentation.
Before sending: Read long architecture descriptions and the full contact line at normal size.
A bold identity band and supporting column separate practical skills from work history.
Before sending: Inspect narrow contact and supporting sections and the copied PDF reading order.
A quiet single-column hierarchy keeps the evidence prominent.
Before sending: Expanded histories still need review of the complete export.
“Use” opens signup with that design and photo preference selected for the builder. A free account is required. Free-plan PDF downloads include a watermark; see current plans for paid options. Photo conventions vary; follow the employer’s instructions and local expectations.
The three designs use the same fictional career. The default has no photo. Follow the employer’s instructions and local conventions; the optional portrait is AI-generated. Signup retains the exact design, supported photo preference and Security Engineer role. It does not insert the example career or portrait into your account. A free account is required, and free-plan PDF downloads include a watermark. These previews show paid-plan output.
Jordan Avery, the employers, qualifications, dates, projects and results are original editorial fiction. The example.com addresses and links and the 555 phone number are illustrative placeholders. Replace every field with your own facts. The optional portrait is AI-generated, and all qualifications and any license or registration dates are fictional and contain no valid identifiers. The base record has two jobs, six experience bullets, one education record and one project.
Security Engineer | Preventive controls and risk reduction evidence
jordan.avery@example.com · +1 614 555 0117
Portfolio: https://example.com/jordan-avery
Security engineer supporting identity controls, configuration reviews and security logging with system owners. Uses Terraform change review and documented checks to track control exceptions. Brings systems-engineering experience and keeps configuration evidence distinct from guarantees about compromise or overall organizational risk.
Identity access controls · Configuration review · Terraform · Security logging · Exception tracking · Change review
Birchgate Infrastructure Services · Raleigh, NC
April 2022–Present
Cedarfield Technology Operations · Raleigh, NC
June 2019–March 2022
Bachelor of Science in Information Technology · Maplecrest University · Raleigh, NC
August 2015–May 2019
Security Engineer · Birchgate Infrastructure Services
June 2026–July 2026
Identity controls · Terraform · Security logs · Exception register
Reconciled 40 agreed configuration checks to 34 meeting the condition and six open exceptions. Retained owner decisions and review evidence without inferring a breach-prevention or complete risk-reduction result.
https://example.com/jordan-avery/configuration-control-evidence-review
Jordan’s fictional Raleigh role reviews identity controls, configuration settings and security logging with system owners. Terraform changes pass permitted testing and owner review. Earlier systems engineering provides operational experience without being retitled as security-program leadership.
The selected bodies span LinkedIn’s staff-level identity architecture, Mirantis corporate security and Delivery Hero product security. Seniority, architecture, detection and application-assessment requirements differ. The sample does not claim all of those responsibilities, penetration-testing experience or professional certifications.
A preventive-control example should show the authorized scope, test environment and approval. Report implemented work separately from planned remediation. Use permitted aggregate descriptions and keep internal configurations, real access details and sensitive findings private.
Read the employer descriptions directly: LinkedIn Staff Software Security Engineer - Identity & Access Management; Mirantis Senior Corporate Security Engineer; Delivery Hero Security Engineer, Product Security team. This selected dated sample illustrates differences in scope and requirements, rather than a representative labor-market survey.
Each after sentence appears in the base career record. The weak before statements are teaching examples. Use the evidence prompts to check the population, decisions and limitations behind your own wording.
Before: Secured the entire organization alone.
After: Review assigned identity-access controls, configuration settings and security-log coverage with system owners, recording approved control definitions and evidence gaps.
Why it works: Bounded controls and collaborators avoid an unprovable organization-wide security claim.
Evidence to check: System scope, control definitions and owners.
Before: Eliminated every security risk.
After: Reviewed 40 approved configuration checks for the assigned service group in June 2026; 34 met the defined condition and six remained documented exceptions.
Why it works: The 85% check-meeting share is not a breach-prevention rate or complete risk reduction.
Evidence to check: Check cohort, conditions, evidence and exception owners.
Before: Deployed every control without review.
After: Review Terraform changes for agreed identity and logging settings, test proposed configurations in the permitted environment and obtain owner approval before implementation.
Why it works: Review and testing are evidence of a controlled process without guaranteeing secure outcomes.
Evidence to check: Terraform changes, test scope and approval record.
Before: Closed every finding instantly.
After: Maintain exceptions with impact context, proposed next actions and accountable owners, distinguishing implemented controls from planned work in status reports.
Why it works: Open exceptions remain visible instead of becoming an invented closure or safety claim.
Evidence to check: Exception register, owner decisions and status.
Before: Ran the entire security program.
After: Maintained approved service configurations and operational logs, checking access-change requests against supplied procedures before senior review.
Why it works: Systems work provides a foundation without inventing security-program authority.
Evidence to check: Procedures, requests and reviewer.
Before: Prevented every incident forever.
After: Documented configuration questions and missing log records for the incoming engineer, preserving timestamps and unresolved dependencies for follow-up.
Why it works: An evidence handover is useful without an incident-prevention guarantee.
Evidence to check: Log references, questions and follow-up owners.
The June assigned service group has 40 approved configuration checks. Thirty-four meet the condition and six remain exceptions, giving an 85% share. This does not measure the probability of compromise or all organizational security risk.
Exception owners, impact context and next decisions remain visible. Terraform review and test evidence show a process; they do not prove every deployed control is effective against every threat or that no incidents can occur.
Use relevant capabilities that your experience or projects demonstrate. The table connects the sample’s claims to records a candidate should check. A skill keyword is not a substitute for an example, and a private employer record should stay private unless sharing is permitted.
| Capability in context | Evidence to check | Sample work |
|---|---|---|
| Define control scope | System scope, control definitions and owners. | Review assigned identity-access controls, configuration settings and security-log coverage with system owners, recording approved control definitions and evidence gaps. |
| Keep configuration results bounded | Check cohort, conditions, evidence and exception owners. | Reviewed 40 approved configuration checks for the assigned service group in June 2026; 34 met the defined condition and six remained documented exceptions. |
| Show preventive change methods | Terraform changes, test scope and approval record. | Review Terraform changes for agreed identity and logging settings, test proposed configurations in the permitted environment and obtain owner approval before implementation. |
| Explain remaining risk | Exception register, owner decisions and status. | Maintain exceptions with impact context, proposed next actions and accountable owners, distinguishing implemented controls from planned work in status reports. |
| Keep systems experience specific | Procedures, requests and reviewer. | Maintained approved service configurations and operational logs, checking access-change requests against supplied procedures before senior review. |
| Connect handovers to evidence | Log references, questions and follow-up owners. | Documented configuration questions and missing log records for the incoming engineer, preserving timestamps and unresolved dependencies for follow-up. |
Jordan’s IT degree and employers are fictional. No CISSP, Security+, vendor credential, clearance or formal audit authorization is supplied. BLS describes varied entry paths and employer certification preferences; verify genuine current qualifications and each role’s actual requirements.
A systems engineer can show approved configuration work, access-request checks and clear log handovers. Keep senior review and authorization boundaries visible.
A clearly labeled synthetic configuration review can show check definitions and exception tracking without accessing real systems. The expanded record preserves Jordan’s internship and correctly attributed work projects.
Only Jordan Avery’s resume email and one portfolio contact URL change in this scenario. Identity, phone, employment, qualifications and projects stay identical. Harbor uses the optional photo-on view here. Read every final character of the email and URL, and check the link destination against the complete record below.
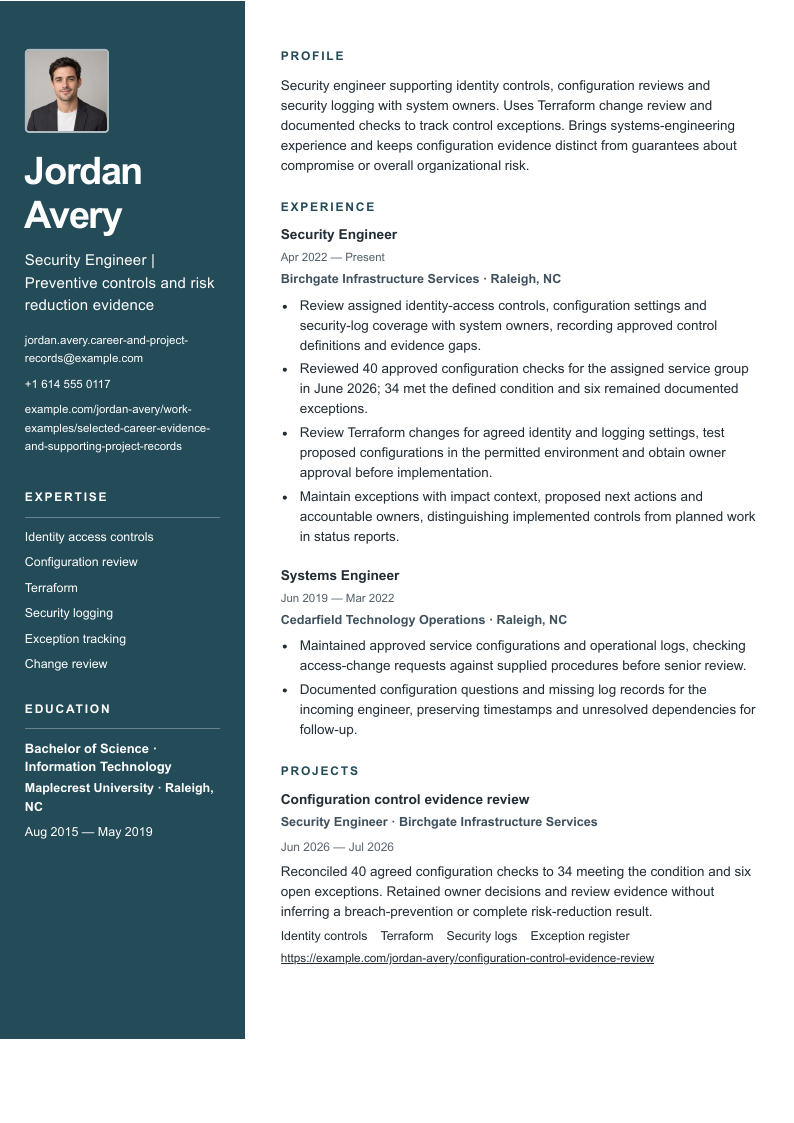 Open page 1 at full size
Security Engineer | Preventive controls and risk reduction evidence
jordan.avery.career-and-project-records@example.com · +1 614 555 0117
Security engineer supporting identity controls, configuration reviews and security logging with system owners. Uses Terraform change review and documented checks to track control exceptions. Brings systems-engineering experience and keeps configuration evidence distinct from guarantees about compromise or overall organizational risk.
Identity access controls · Configuration review · Terraform · Security logging · Exception tracking · Change review
Birchgate Infrastructure Services · Raleigh, NC
April 2022–Present
Cedarfield Technology Operations · Raleigh, NC
June 2019–March 2022
Bachelor of Science in Information Technology · Maplecrest University · Raleigh, NC
August 2015–May 2019
Security Engineer · Birchgate Infrastructure Services
June 2026–July 2026
Identity controls · Terraform · Security logs · Exception register
Reconciled 40 agreed configuration checks to 34 meeting the condition and six open exceptions. Retained owner decisions and review evidence without inferring a breach-prevention or complete risk-reduction result.
https://example.com/jordan-avery/configuration-control-evidence-review
The expanded Harbor scenario keeps the photo off. It preserves every base field and adds one earlier job and two projects. Project titles and employers reflect the job actually held during their dates, and method lists describe the work in that project. Read the full record, including the final project and its limits.
Condense repeated responsibilities before removing information a reader needs to understand a claim. Review headings, dates and continuation pages after your own changes; the design name alone cannot establish how an expanded career will read.
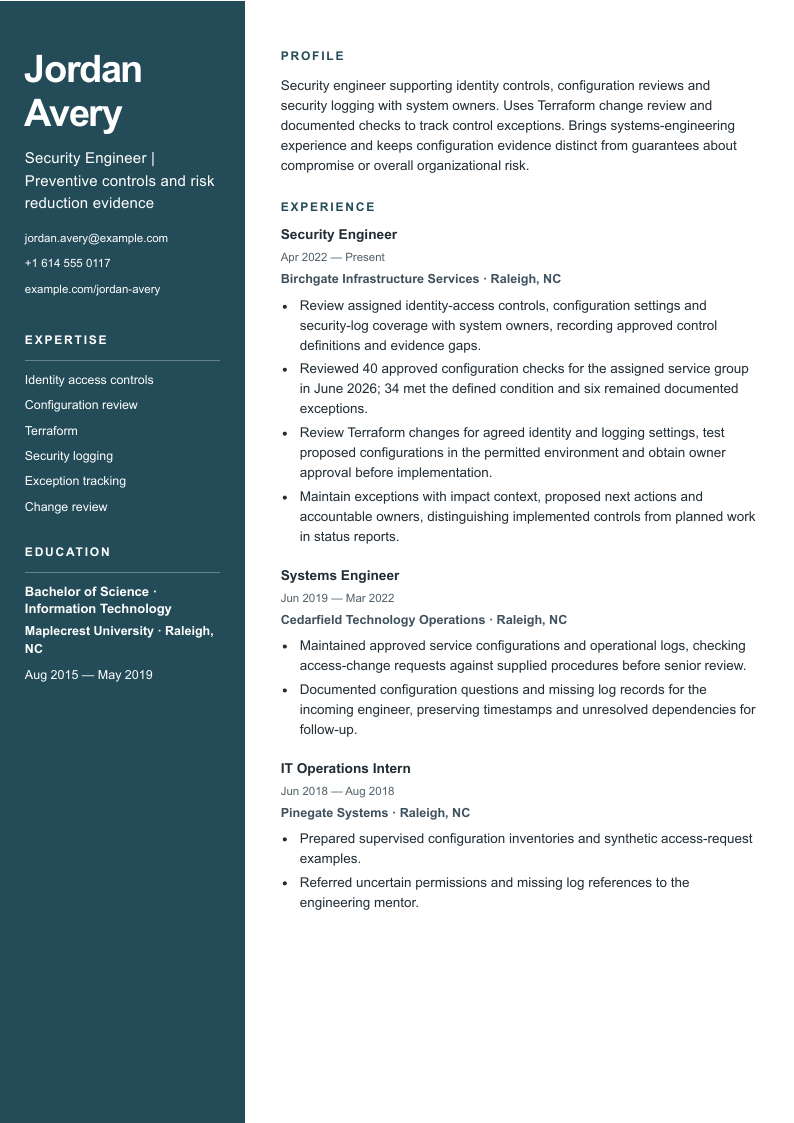 Open page 1 at full size
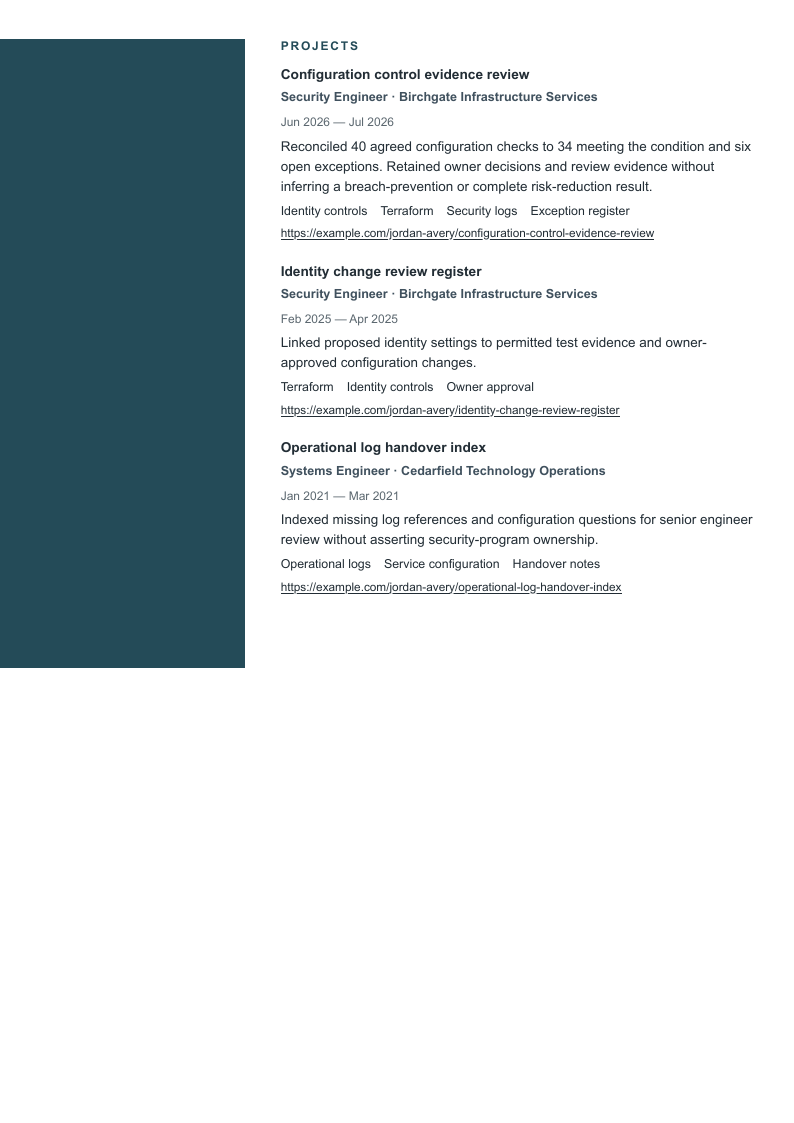 Open page 2 at full size
Security Engineer | Preventive controls and risk reduction evidence
jordan.avery@example.com · +1 614 555 0117
Portfolio: https://example.com/jordan-avery
Security engineer supporting identity controls, configuration reviews and security logging with system owners. Uses Terraform change review and documented checks to track control exceptions. Brings systems-engineering experience and keeps configuration evidence distinct from guarantees about compromise or overall organizational risk.
Identity access controls · Configuration review · Terraform · Security logging · Exception tracking · Change review
Birchgate Infrastructure Services · Raleigh, NC
April 2022–Present
Cedarfield Technology Operations · Raleigh, NC
June 2019–March 2022
Pinegate Systems · Raleigh, NC
June 2018–August 2018
Bachelor of Science in Information Technology · Maplecrest University · Raleigh, NC
August 2015–May 2019
Security Engineer · Birchgate Infrastructure Services
June 2026–July 2026
Identity controls · Terraform · Security logs · Exception register
Reconciled 40 agreed configuration checks to 34 meeting the condition and six open exceptions. Retained owner decisions and review evidence without inferring a breach-prevention or complete risk-reduction result.
https://example.com/jordan-avery/configuration-control-evidence-review
Security Engineer · Birchgate Infrastructure Services
February 2025–April 2025
Terraform · Identity controls · Owner approval
Linked proposed identity settings to permitted test evidence and owner-approved configuration changes.
https://example.com/jordan-avery/identity-change-review-register
Systems Engineer · Cedarfield Technology Operations
January 2021–March 2021
Operational logs · Service configuration · Handover notes
Indexed missing log references and configuration questions for senior engineer review without asserting security-program ownership.
https://example.com/jordan-avery/operational-log-handover-index
Review your resume with the analyzer and check every suggestion against your records. No template guarantees parsing, ranking, an interview or a hiring outcome. A free account is required for the builder; free-plan PDF downloads include a watermark. The examples show paid-plan output.
Report the defined check population and remaining exceptions. A compliance-style check result is not complete risk elimination.
Only genuine relevant credentials with accurate current status. None are invented here.
Use permitted descriptions and protect sensitive systems and access information. Explain your authorized contribution and review process.
Signup retains the exact design, the supported photo setting and Security Engineer role. Compact stays photo-free. The fictional career and portrait are not inserted into your account. A free account is required and free-plan PDF downloads include a watermark.
Prepared by Resumize with AI-assisted research and drafting for English-language US resume context. Employer descriptions from other markets are identified in the discussion and notes. Full employer bodies were checked October 30, 2026; availability, location eligibility and engagement conditions vary and can change. The original fictional records are teaching material, not verified applicants or evidence that this candidate meets every opening. No application was submitted or hiring outcome tested.
Official occupational and credential guidance was reviewed through direct, web-access or indexed text as stated in each note. Retrieval failures remain disclosed. The source notes distinguish these limits from full direct employer retrieval.
Read October 30, 2026. LinkedIn, Mountain View, US; staff-level identity/access architecture and software security, broader and more senior than the sample’s control-review remit. Complete primary role body retrieved. Application instructions/controls were present; availability may change.
Read October 30, 2026. Mirantis, US remote; corporate security, identity, endpoint and detection responsibilities. The page title says Senior Corporate Security Engineer while the body uses Corporate Security Engineer. Complete primary role body retrieved. Application instructions/controls were present; availability may change.
Read October 30, 2026. Delivery Hero, Berlin, Germany; product-security role. Application assessment, threat modeling and scanner experience in this posting are not silently assigned to the fictional preventive-control record. Complete primary role body retrieved. Application instructions/controls were present; availability may change.
Official web-access body reviewed October 30, 2026 after direct retrieval returned 403. Adjacent security occupation, varied entry paths and employer certification preferences; not a certification supplied to the fictional record.